Roles and permissions for desk and room booking
Gingco Share, our resource management software, comes with a dedicated roles and permissions model built around the needs of your organization. Permissions follow the need-to-know principle and can be restricted by user group, resource group and location. Role-based permissions give you a permission model that is audit-ready, transparent, easy to maintain and aligned with works council requirements. Role-based access control (RBAC) means that users do not receive permissions individually, but through roles that reflect their tasks and responsibilities. In desk and room booking software, roles define who can view, book, book on behalf of others, approve, manage or administer desks, rooms, parking spaces and other resources, and at which locations. Gingco Share combines more than 150 individual permissions into roles that can be restricted by users, resources and locations.
- Need-to-know principle for every permission
- Permissions by user group, resource group and location
- Audit-ready and works-council-compliant
A permission model as individual as your organization
Complex, dynamic, effective and goal-oriented: the right permission model strikes the best possible balance between security, transparency and productivity.
From clear goals and legal requirements to naming conventions, responsibilities and user and permission management, we look at every building block of your setup and design a holistic permission model with you. That includes a well-designed roles and permissions structure, special permissions and the secure integration of technical interfaces.
Throughout, we follow the need-to-know principle: people only get access to the data that is relevant to their tasks and responsibilities.
„Getting the balance right is what matters. Permissions that are too restrictive hurt adoption and productivity, while permissions that are too broad create unnecessary security risks.“
With many years of experience working with international customers, we understand the complex requirements of organizations across industries and of all sizes. On this basis, we develop a permission model with you that fits your processes and requirements, for strong security today and a setup that is built to last.
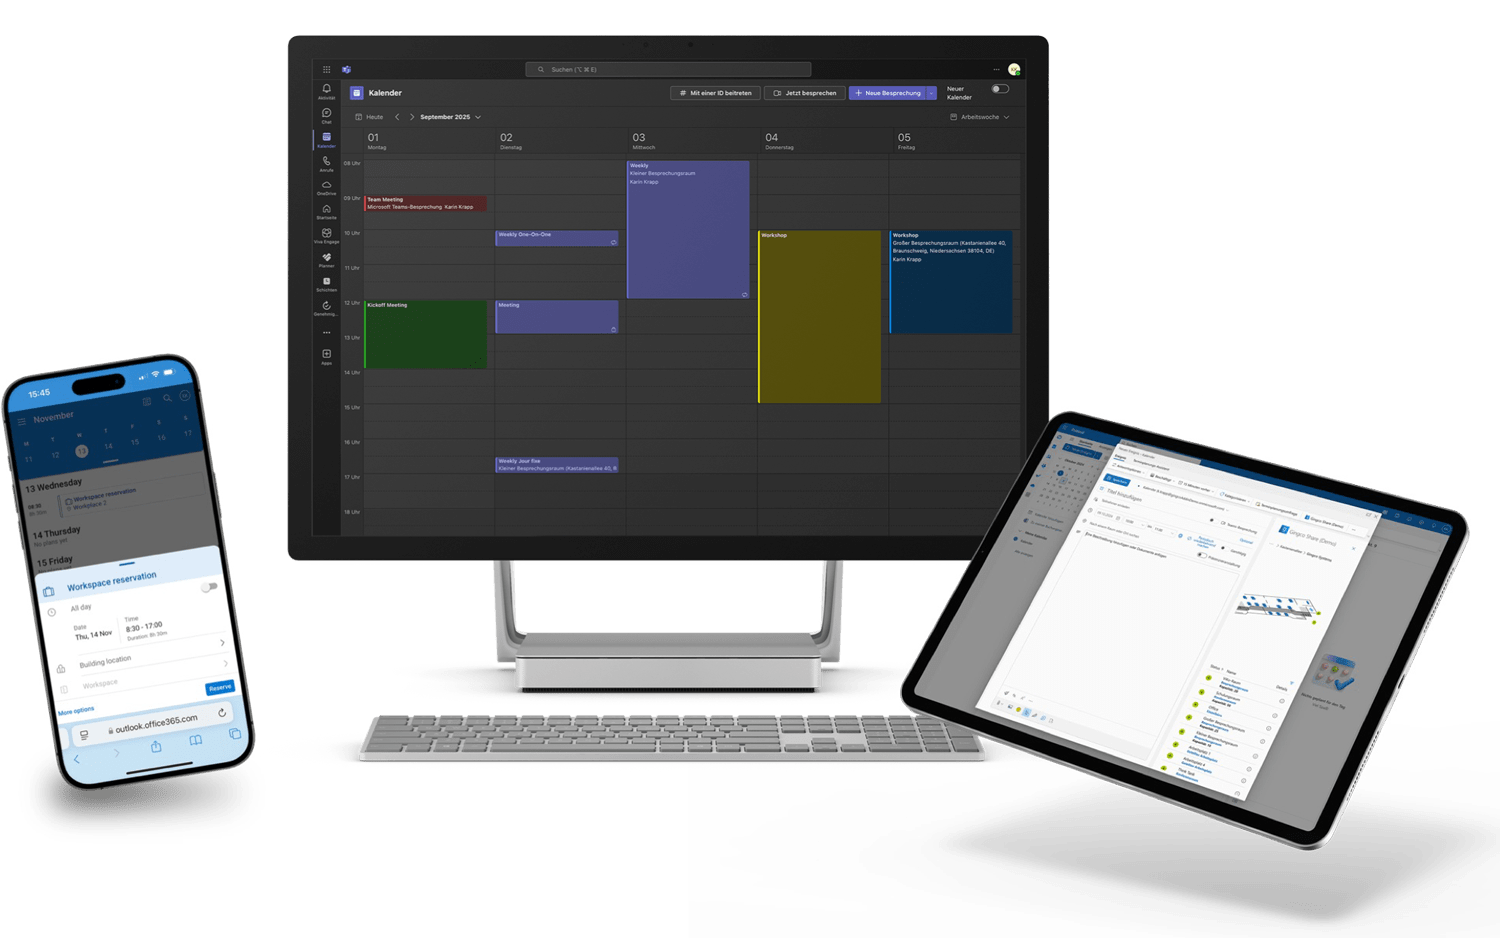
Bidirectional Exchange synchronization
Role-based access control with more than 150 individual permissions
More than 150 individual permissions can be assigned to roles and permission groups. Each of them can be restricted along three core dimensions: users, resources and locations. The result is a permission model tailored precisely to your organization. With role-based assignment, every user gets exactly the system access that matches their tasks, responsibilities and approvals.
Our predefined global, local and functional permission groups give you a proven starting point. You can adapt and extend them flexibly to fit your organizational structure and processes. Individual permissions can be moved between permission groups and combined into new roles.
Permissions are structured hierarchically: higher-level roles inherit all permissions of the groups below them and add permissions of their own.
- More than 150 individual permissions, scoped by users, resources and locations
- Global, local and functional permission groups as a flexible foundation
- Roles inherit the permissions of lower-level groups and add their own
Social desk sharing and works council compliance
Gingco Share helps you implement workplace concepts that meet works council and data protection requirements, while upholding the organizational and company policies that protect employee rights.
In line with employees' rights to information and co-determination, each person decides for themselves who can see their booking data.
- Supports workplace concepts that meet works council and data protection requirements
- Protects employee rights in line with your company policies
- Employees control who can see their booking data
Automated role assignment by department, AD group or cost center
Principle of least privilege: minimal access, maximum focus
No automatic full access, not even for managers
Role-based access to data and limiting personal information to authorized users help you put your internal data protection policies and works agreements into practice.
Even employees with high security clearance or in leadership roles can't access sensitive data unless they need it and are authorized to see it.
A clear permission structure, with restricted permissions and limited access to certain system areas, protects employees from the consequences of accidental actions. At the same time, usage stays transparent and respects co-determination rights, because employees decide for themselves who can see their booking data.
Role-based access for regulated industries and critical infrastructure
Manufacturing, retail, IT, banking or critical infrastructure: every company and public authority has its own requirements for security and access permissions. The goal is always the same: reliably protect sensitive data and information, prevent misuse and industrial espionage, and minimize potential damage from cyberattacks or unauthorized users.
Our role-based permission model gives you the right foundation. It lets you control access rights precisely by role and responsibility, so users get exactly the permissions they need for their work. This is how Gingco Share supports the need-to-know principle your organization already has in place.
Consistent permissions across devices, clients and systems
Permission models have to meet a wide range of requirements, and IT trends such as cloud, BYOD, AI and IoT make this even more challenging.
No matter which service or device is used, your security policy must be enforced and your permission model must apply. That's why ours scales with you and applies consistently across clients and systems.
GDPR and ISO/IEC 27001
Smart user and permission management with automated onboarding and offboarding
Gingco Share connects to your existing services, identity providers and HR systems. Our automated user provisioning makes user and role management simple and efficient.
Employee, organizational and location data is taken from your source systems and kept in sync. Organizational changes are reflected automatically, which keeps manual configuration in Gingco Share to a minimum. You continue to manage your source data centrally in your existing systems.
Automated user onboarding and offboarding
Automated onboarding and offboarding processes grant and revoke permissions quickly, reliably and dynamically. Roles, access rights and user accounts stay up to date, consistent and secure at all times.
You decide not only when user accounts are deleted, but also how a person’s bookings are handled, both in general and when their account is deleted.
Anonymize or delete booking data automatically
Depending on your company’s requirements, such as works agreements, data protection policies or legal retention periods, personal booking data can be anonymized or deleted automatically after defined periods. You stay in full control and can keep booking data for statistical analysis while the personal reference is removed.
Tailored to your compliance requirements
Everything is configured to your organization’s specific requirements for data protection, works council, compliance, monitoring, auditing and reporting, as well as your organizational and business context. This is how Gingco Share puts your data protection and compliance policies into practice, including for historical booking data.
Frequently asked questions
Why do we need a role-based permission model?
A role-based permission model is the foundation of any hybrid work environment. Not everyone should be able to see or manage the same rooms, features and data. A role-based model protects sensitive booking data in line with the GDPR, reduces the risk of user errors and misuse, establishes clear responsibilities and traceable changes, and keeps the interface clean, because everyone only sees what is relevant to them.
Can the permission model be adapted to our organizational structure?
Can we separate tenants and legal entities?
Can Gingco Share be used in compliance with the GDPR and works council requirements?
Yes. Gingco Share supports GDPR-compliant processes and works council requirements through role-based access, transparent data processing, defined anonymization and deletion concepts, and reports configured in line with your works agreements. Usage stays transparent, with clear responsibilities and controlled access rights.
Which personal data is processed?
Only the information required for the booking process, such as name and organizational unit.
Can individual usage profiles be created?
Gingco Share offers various analyses and reports. Your organization controls which of them are permitted under your data protection policies and works agreements.